Automate Third-Party Cybersecurity Questionnaires with Panorays
Hundreds of Teams Trust Panorays to Manage Vendor Risk
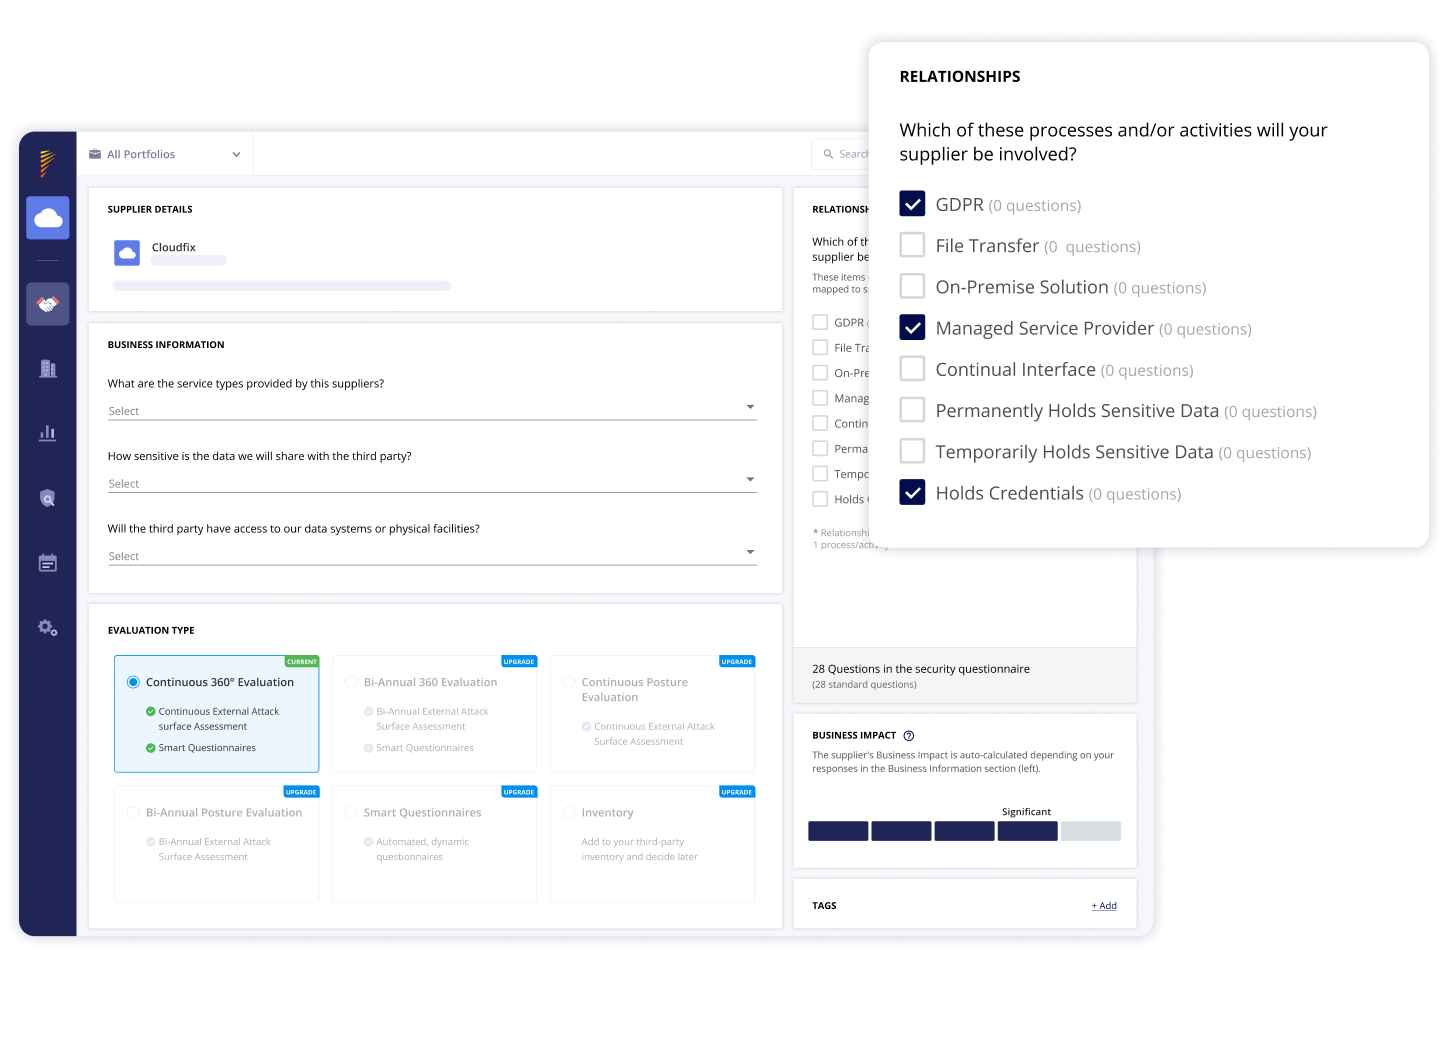
Customized Third-Party Cybersecurity Questionnaires
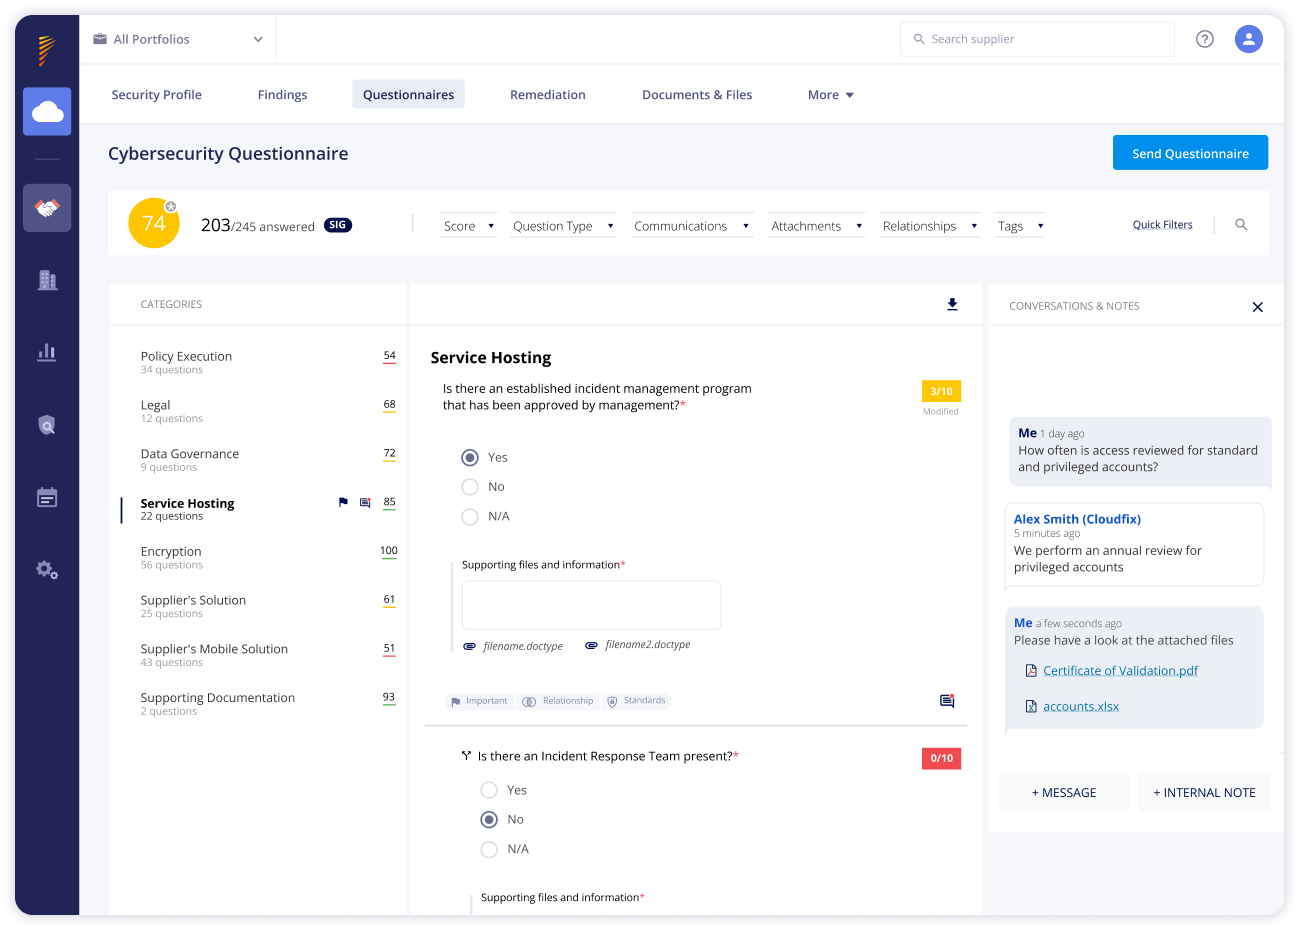
Simplify vendor assessments with Panorays’ customized questionnaires tailored to your specific vendor relationships and their business impact. With our auto-generated questionnaire templates, you can concentrate on the questions that really matter.
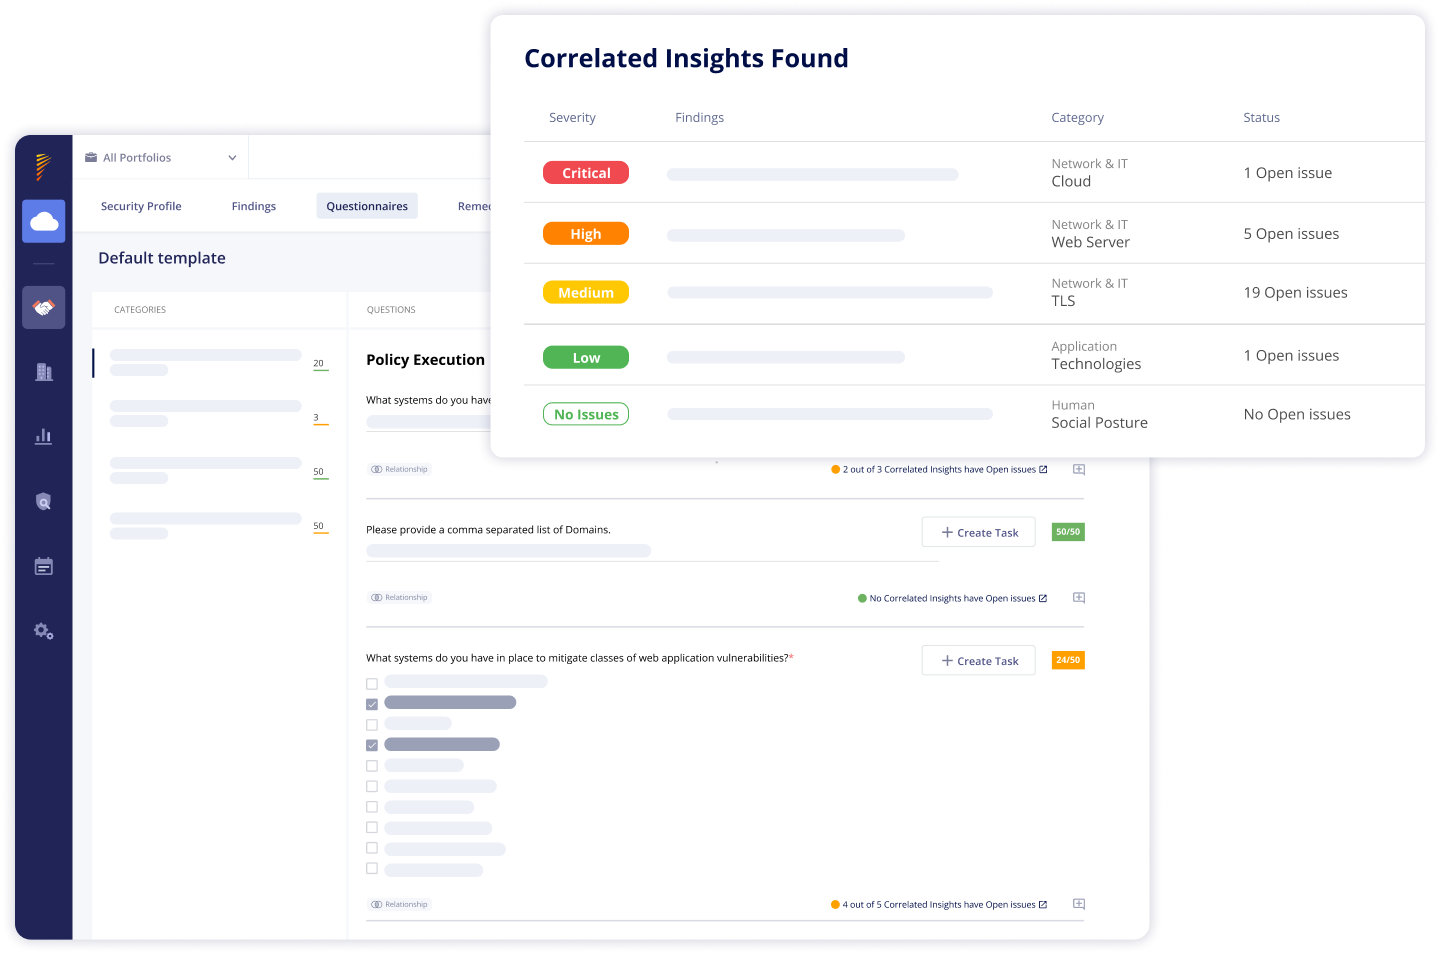
Validated Cybersecurity Questionnaire Responses
Panorays validates questionnaire responses by comparing them with vendors’ external documents and cyber posture assessments. Any gaps are then highlighted, making it simple to review and address them.
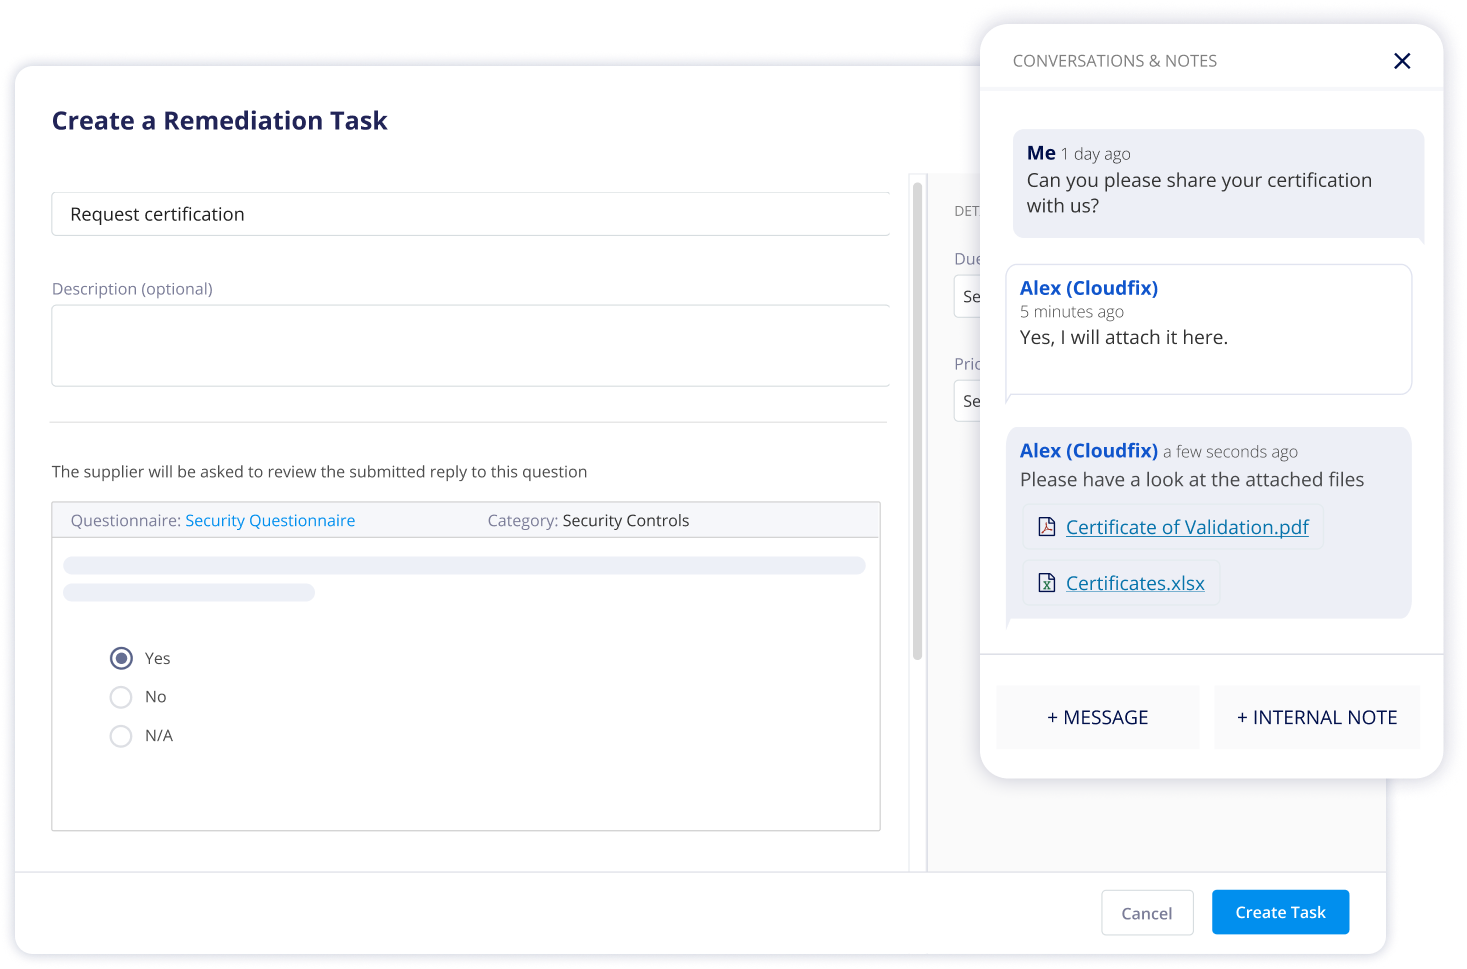
Effortless Third-Party Collaboration
Panorays streamlines collaboration with your third-parties by transforming questionnaire responses into automated tasks. You can effortlessly establish due dates, receive timely reminders, and engage in convenient in-app chats for effective communication with your external vendors.
Automate, Validate and Scale
Cybersecurity Questionnaires
Ensure Regulation Compliance
Efficiency at Scale
Collaboration Made Simple
Accelerated Responses
Four Steps to Seamlessly Manage Vendor Questionnaires
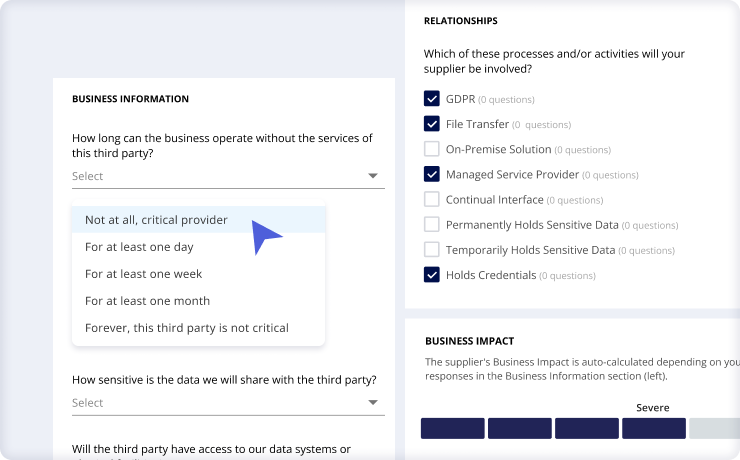
Step 1: Customize Questionnaires
Build questionnaires from industry standard templates, or create unique questions based on third-party criticality.
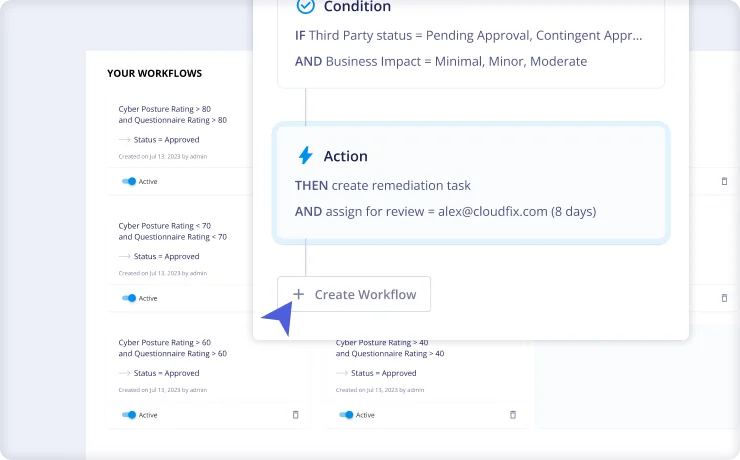
Step 2: Automate Questionnaire Workflows
Set up questionnaire workflows to automatically create remediation tasks, assign teammates, and approve or reject certain vendors based on their scores.
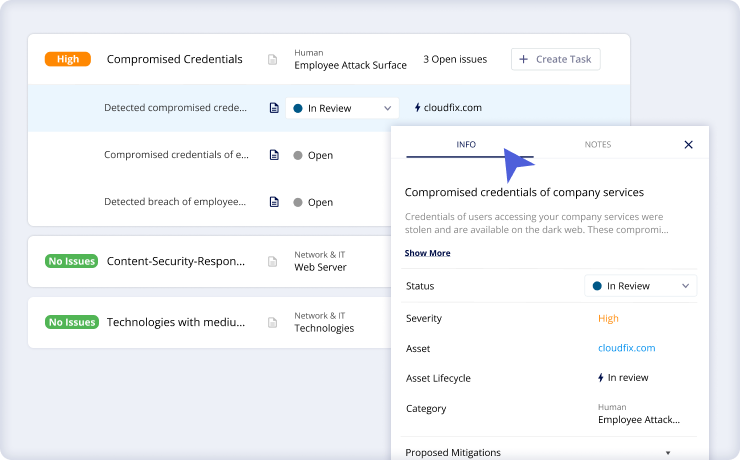
Step 3: Validate Vendor Responses
Cross-reference vendor responses with cyber posture data and vendor documentation to get a comprehensive view of third-party risks.
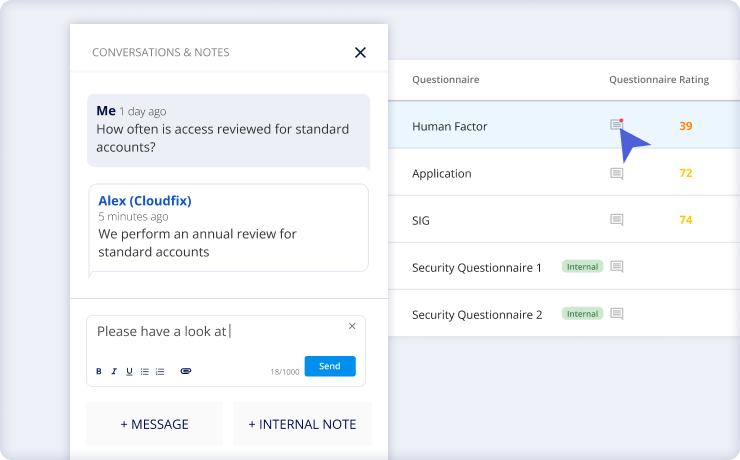
Step 4: Resolve Cybersecurity Gaps
Communicate with vendors to resolve any security gaps and keep track of all open tasks in an interactive management inventory.
-
Step 1: Customize Questionnaires
Build questionnaires from industry standard templates, or create unique questions based on third-party criticality.
-
Step 2: Automate Questionnaire Workflows
Set up questionnaire workflows to automatically create remediation tasks, assign teammates, and approve or reject certain vendors based on their scores.
-
Step 3: Validate Vendor Responses
Cross-reference vendor responses with cyber posture data and vendor documentation to get a comprehensive view of third-party risks.
-
Step 4: Resolve Cybersecurity Gaps
Communicate with vendors to resolve any security gaps and keep track of all open tasks in an interactive management inventory.
Key Vendor Questionnaire Features

Built-in SIG and CAIQ Questionnaires

Custom Questionnaire Templates

Customized Risk Assessments

Automatic Vendor Evaluations

Validated Responses

Easy-to-Manage Workflows
Cybersecurity Questionnaire Frequently Asked Questions
-
A third-party cybersecurity questionnaire is a structured assessment used by organizations to evaluate the security, privacy, and compliance controls of external vendors, suppliers, and service providers. It gathers critical details regarding a vendor’s data protection policies, access controls, incident response capabilities, and technical safeguards to ensure they meet your organizational security standards.
-
A comprehensive questionnaire should cover key security domains, including access management, encryption standards, network security, incident response, vulnerability management, physical security, and regulatory compliance (such as GDPR or SOC 2). Questions should evaluate both operational policies and technical implementations to provide an accurate representation of the vendor’s security baseline.
-
Vendors typically complete assessments during initial onboarding and then on a recurring basis—usually annually. However, high-risk vendors or those with access to sensitive systems and data should be assessed more frequently, or triggered automatically whenever significant changes occur in the vendor’s contract scope, regulatory environment, or security posture.
-
Organizations automate questionnaires by adopting dedicated Third-Party Cyber Risk Management (TPCRM) platforms like Panorays. Automation replaces manual tracking by automatically scheduling distributions, auto-filling recurring vendor responses, assigning remediation tasks, and tracking completion status through centralized dashboards.
-
AI accelerates the assessment lifecycle for both security teams and vendors. For vendors, AI engines analyze past questionnaire submissions and internal documentation to suggest accurate answers automatically. For evaluating teams, AI cross-references vendor answers against uploaded evidence, such as SOC 2 reports and ISO certifications, verifying claims instantly and highlighting discrepancies for human review.
-
A vendor security questionnaire is a self-reported tool used to collect specific data about a vendor’s internal controls. A vendor risk assessment is the broader, holistic process of analyzing that questionnaire alongside external threat intelligence, technical attack surface data, business criticality, and compliance requirements to determine the vendor’s overall risk impact on your organization.
-
Common industry frameworks integrated into security questionnaires include the NIST Cybersecurity Framework (CSF), ISO/IEC 27001, CIS Controls, and shared assessment standards like the SIG (Standardized Information Gathering) and CAIQ (Consensus Assessments Initiative Questionnaire). Panorays provides pre-built templates based on these frameworks alongside customizable options.
-
Questionnaires provide internal visibility into vendor governance, policies, and administrative safeguards that cannot be detected through external technical scanning alone. When combined with continuous external monitoring, they establish a complete, multi-layered view of a third party’s overall security posture.
-
Regulators across industries (enforcing standards like GDPR, DORA, HIPAA, and PCI DSS) require organizations to demonstrate active oversight of their vendor ecosystems. Security questionnaires provide documented, audit-ready proof that an organization performs due diligence and enforces compliance controls across its supply chain.
-
Once submitted, responses are validated against supporting documentation and external cyber posture metrics. Any identified security gaps or policy deficiencies are flagged as risk items, automatically triggering remediation workflows where security teams and vendors collaborate directly within the platform to resolve issues.
-
Vendors should be tiered based on business impact, data sensitivity, and level of system access. High-risk vendors—such as cloud infrastructure providers or those handling confidential customer data—receive more extensive, frequent questionnaires and deeper technical reviews, while low-risk suppliers complete condensed assessments.
-
Yes. Panorays allows organizations to tailor questionnaires dynamically according to vendor tier, business relationship, and criticality. You can adjust question weighting, define specific “deal-breaker” criteria, and trigger conditional follow-up questions based on vendor answers, ensuring assessments stay relevant without burdening low-risk suppliers.