
How it works
Third-Party Cyber Risk Management Platform
Panorays is with you every step of the way, helping you evaluate new third-parties, close their cyber gaps and continuously monitor their cyber posture.
Accuracy and automation are the name of the game. Here is a quick overview of how Panorays works, giving you full visibility into, and control of, vendor security risk.
01
Analysis
Analyze supplier risk from every angle with inside-out and outside-in data, delivering context-based ratings and actionable insights to help you prioritize what matters most.
Inside-Out
Panorays manages customizable questionnaires that consider internal company policy while aligning with regulations such as GDPR, CCPA and NYDFS.
Outside-In
Panorays mimics thousands of hackers performing reconnaissance to uncover the company’s attack surface. The platform views network and IT, application and human layers.
Panorays
Big Data
Context-Based Ratings
Ratings consider the business and technology relationship with your suppliers, giving more weight to those who are critical to your operations.
- Risk Rating
- Business Impact
Actionable Insights
Panorays pinpoints affected assets and provides detailed descriptions of cyber gaps, along with easy-to-follow instructions for remediation.
Findings
02
Engagement
Business engagement must be friction-free. Collaborate seamlessly with third parties to resolve issues all within the Panorays platform.
03
Remediation
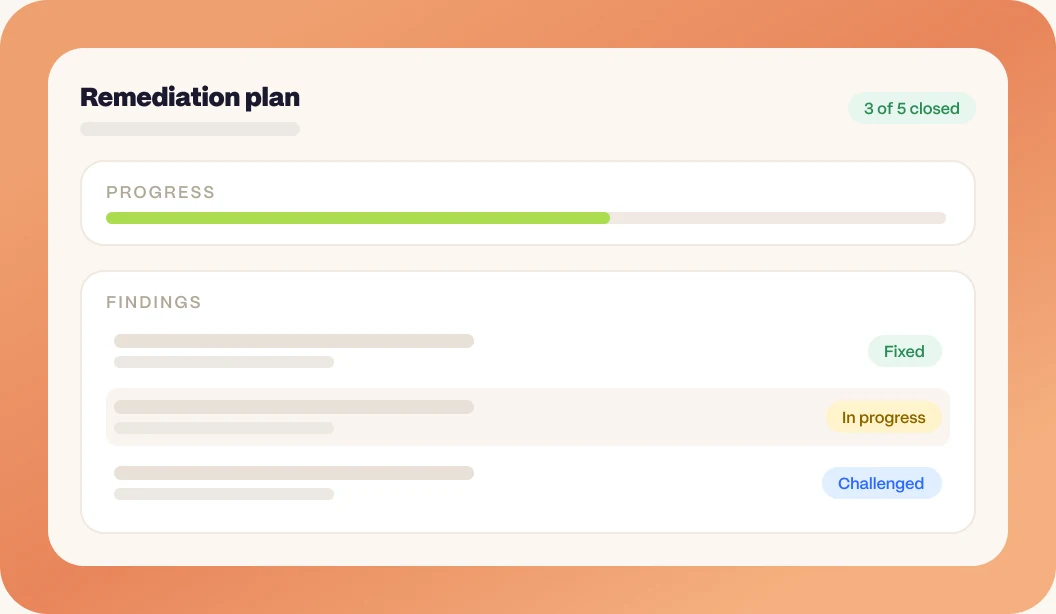
Validate findings with suppliers, challenge answered questions, get guidance to mitigate cyber gaps, and track remediation progress.
04
Approval
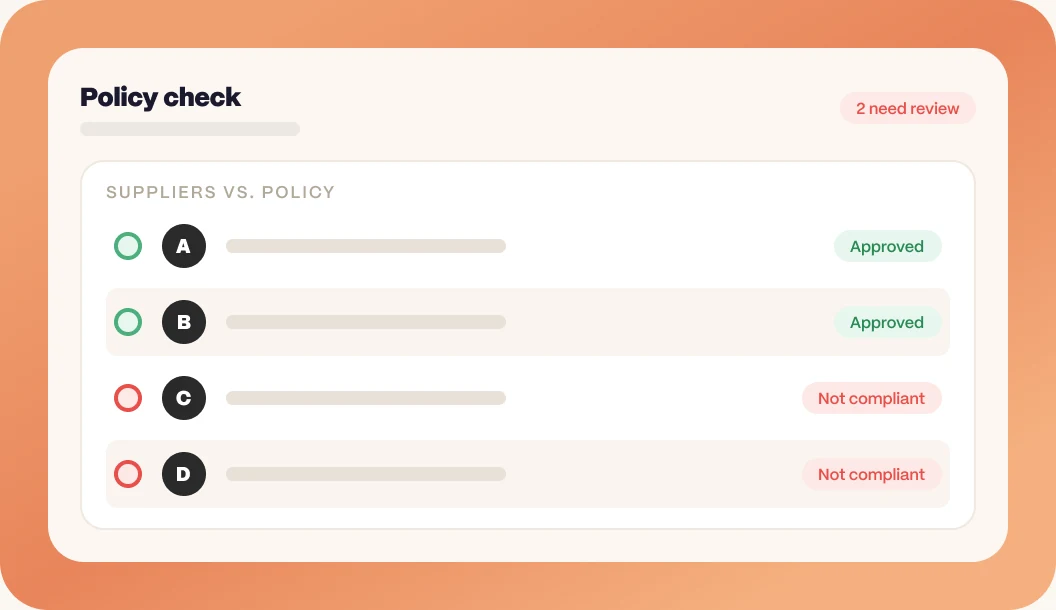
Instantly identify suppliers that don’t meet your company’s security policies.
05
Monitoring
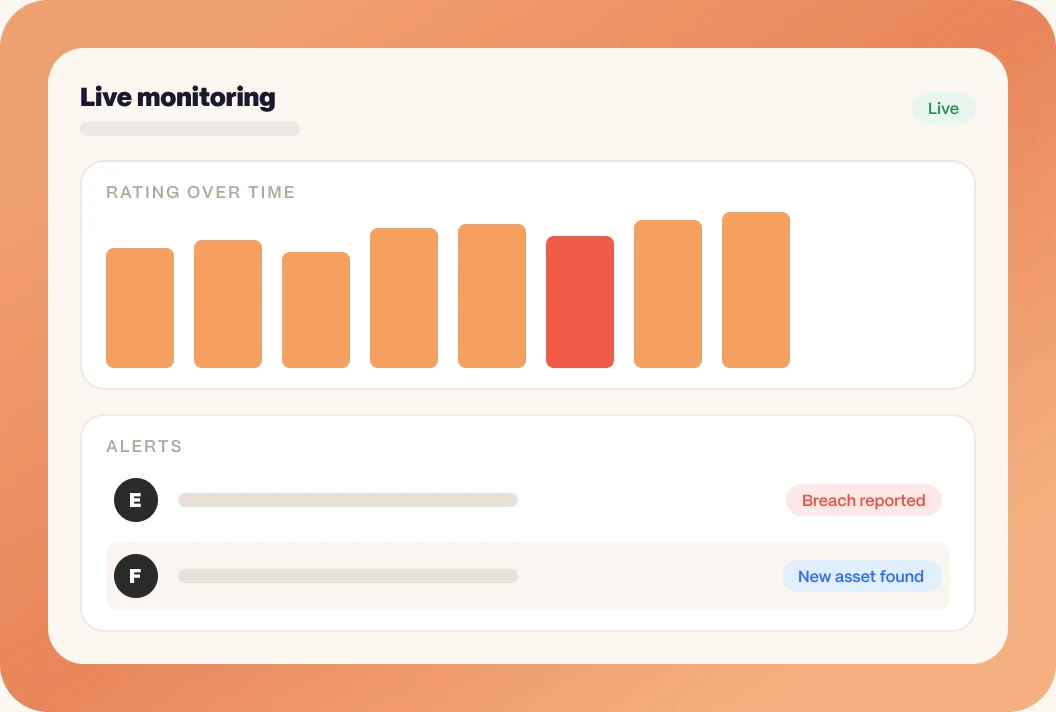
Panorays continuously uncovers and evaluates suppliers with real-time alerts on security changes and breaches.
Related Resources
 Panorays News
Panorays for Microsoft Sentinel: Surfacing Third-Party Intelligence Into the SOC
It’s late, and an analyst in your SOC is investigating an alert. Unusual activity is coming through an integration connected to one…
7 min read
 Breaches, Vulnerabilities & Incident Response
Freezer Hacks Spread Across Europe, Exposing the Growing Cost of Third-Party Cyberattacks
More than 100 European stores have been affected by attacks on refrigeration systems, following a similar incident in France just weeks earlier.…
10 min read
Breaches, Vulnerabilities & Incident Response WordPress Vulnerability CVE-2026-119977: What It Means for Your Vendors’ Websites
On 3 November 2026, CISA added a WordPress vulnerability, CVE-2026-119977, to its Known Exploited Vulnerabilities catalog and gave federal agencies until 6…
8 min read