If you are involved with InfoSec, IT risk or digital supply chain management, then you know that the key to minimizing your risk of third-party breaches is to implement a comprehensive and efficient third-party security risk management (TPCRM) process. But what’s the best way to do it?
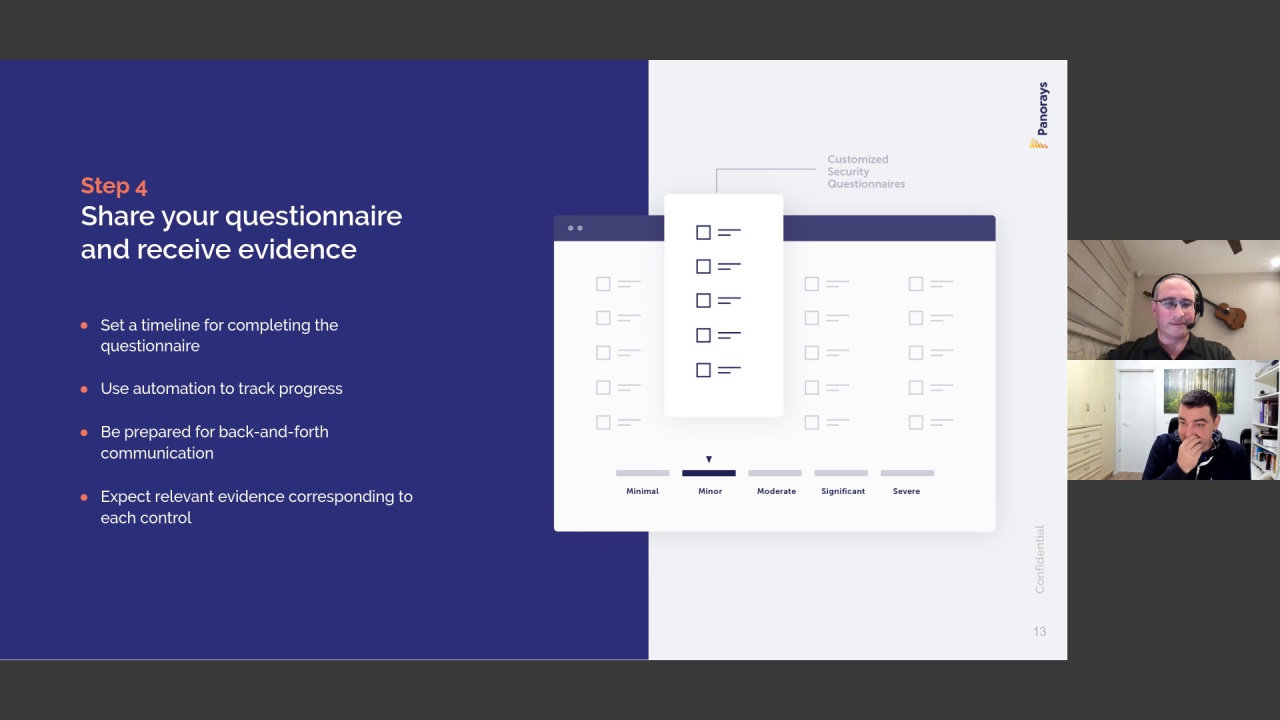
Demi Ben-Ari and Dov Goldman will continue the series on TPCRM Fundamentals and explain the basics about implementing a rapid and robust third-party security management process. You’ll learn how an automated solution helps you:
- Perform third-party evaluations based on the inherent risk of each relationship
- Achieve transparency into third parties’ security practices
- Identify warning signs of a digital supply chain breach
- Collaborate with third parties to ensure successful remediation