
Quantify Third-Party Cyber Risk in Financial Terms
Go Beyond Risk Identification to Understand Financial Impact
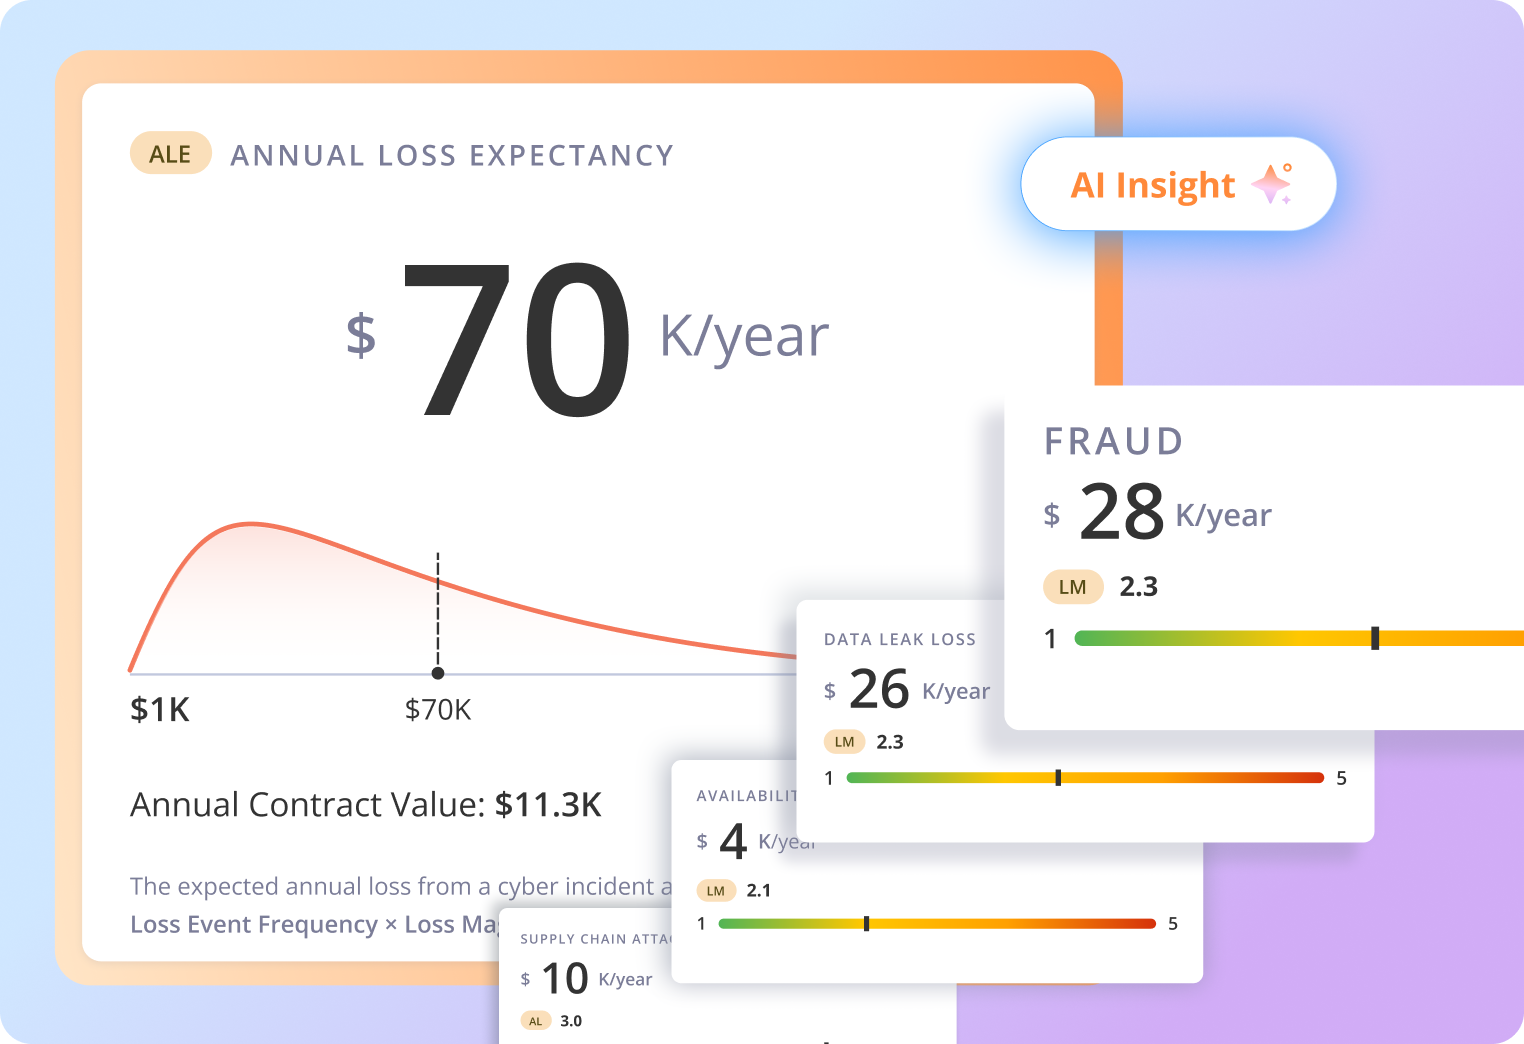
Panorays Cyber Risk Quantification (CRQ) translates third-party cyber risk into clear financial impact. Powered by the industry-recognized Open FAIR™ framework and the supplier intelligence already available in Panorays, CRQ calculates potential annual financial losses across key cyber risk scenarios. This gives security and business leaders the financial context they need to prioritize risk, guide investments, and make more informed decisions.
Ready out of the box financial models. Flexible to your business.
Go Beyond Risk Identification to Understand Financial Impact
You know which suppliers carry cyber risk through High, Medium, Low (or 1–5) ratings. Now take it a step further and show your board how much that risk could actually cost the business.
Panorays CRQ bridges the gap between technical cyber risk and financial decision-making. Quantify potential losses across your third-party ecosystem so security, risk, finance, and executive teams can make decisions using a shared language: financial impact.
Know the Cost of Third-Party Cyber Risk Before It Impacts Your Business
See the potential financial impact of 4 critical third-party cyber scenarios. Powered by Open FAIR™, CRQ uses existing supplier intelligence to estimate each scenario’s likelihood and financial impact, delivering an Annualized Loss Expectancy (ALE) in concrete financial terms.
Availability Loss
Data Leak Loss
Fraud Loss
Supply Chain Attack Loss
From Supplier Intelligence to Financial Risk, In One Platform
Panorays CRQ puts the supplier intelligence already in your platform to work, turning existing third-party cyber risk data into clear, explainable financial insights, without adding another standalone assessment process.
1. Put Your Existing Supplier Intelligence to Work
CRQ draws on the data already available in Panorays, including security posture, questionnaires, business context, relationship data, external exposure, certifications, cyber intelligence, and custom risk factors.
2. Quantify risk without the data burden
Skip rigid data requirements as AI automatically analyzes diverse third-party intelligence across sources and formats, turning the data you already have into financial risk insights without manual preparation, predefined templates, or additional effort.
3. Understand What’s Behind the Estimate
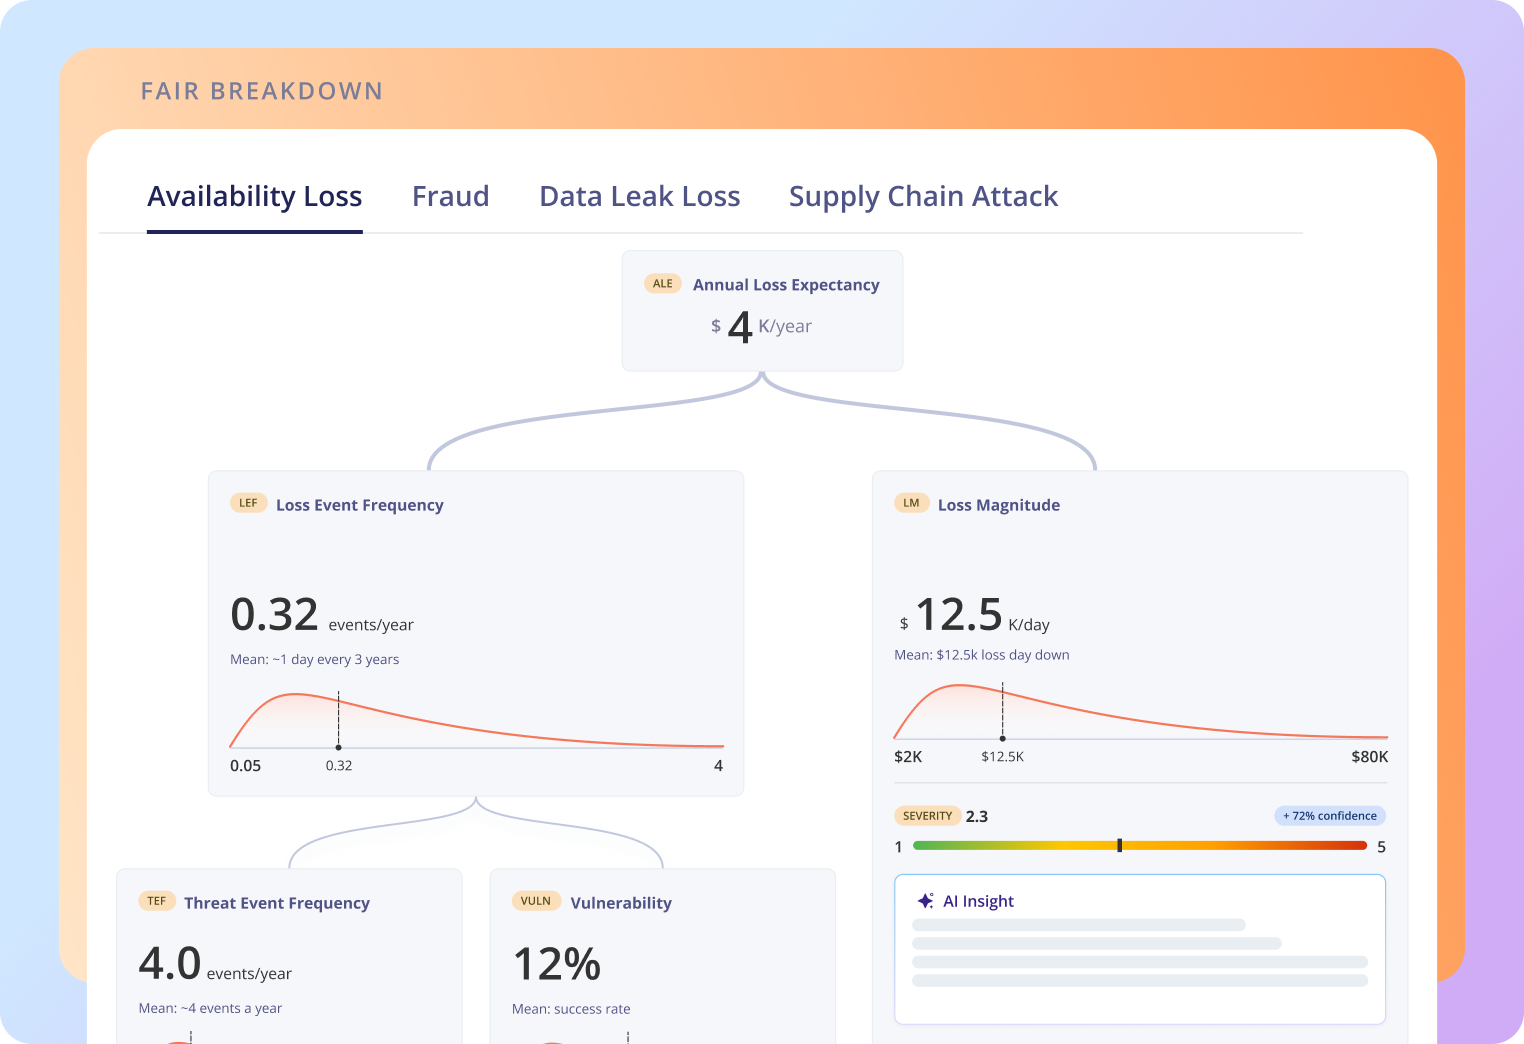
Go beyond a single number with transparent, explainable insights into the factors driving each estimate. Realistic financial ranges account for uncertainty, giving teams the context they need to understand and confidently act on the results.
Frequently Asked Questions
-
Cyber Risk Quantification (CRQ) translates cyber risk into estimated financial impact, helping organizations understand what cyber risk could cost the business.
-
Panorays applies the FAIR methodology to the supplier intelligence you already have—posture, questionnaires, and business context—to estimate the likelihood and financial impact of third-party cyber risk, giving you an expected annual loss with a realistic range.
-
ALE (Annualized Loss Expectancy) estimates how much a cyber risk could cost you in a typical year. It combines the likelihood of an event with its potential financial impact, giving you a dollar figure instead of an abstract risk score.
-
Panorays quantifies four scenarios: Data Leak, Fraud, Availability Disruption, and Supply Chain Attack.
-
CRQ uses existing supplier intelligence in Panorays, including security posture, questionnaires, business context, relationships, and external risk signals.
-
No, CRQ leverages existing Panorays intelligence without requiring additional supplier assessments or data collection.
-
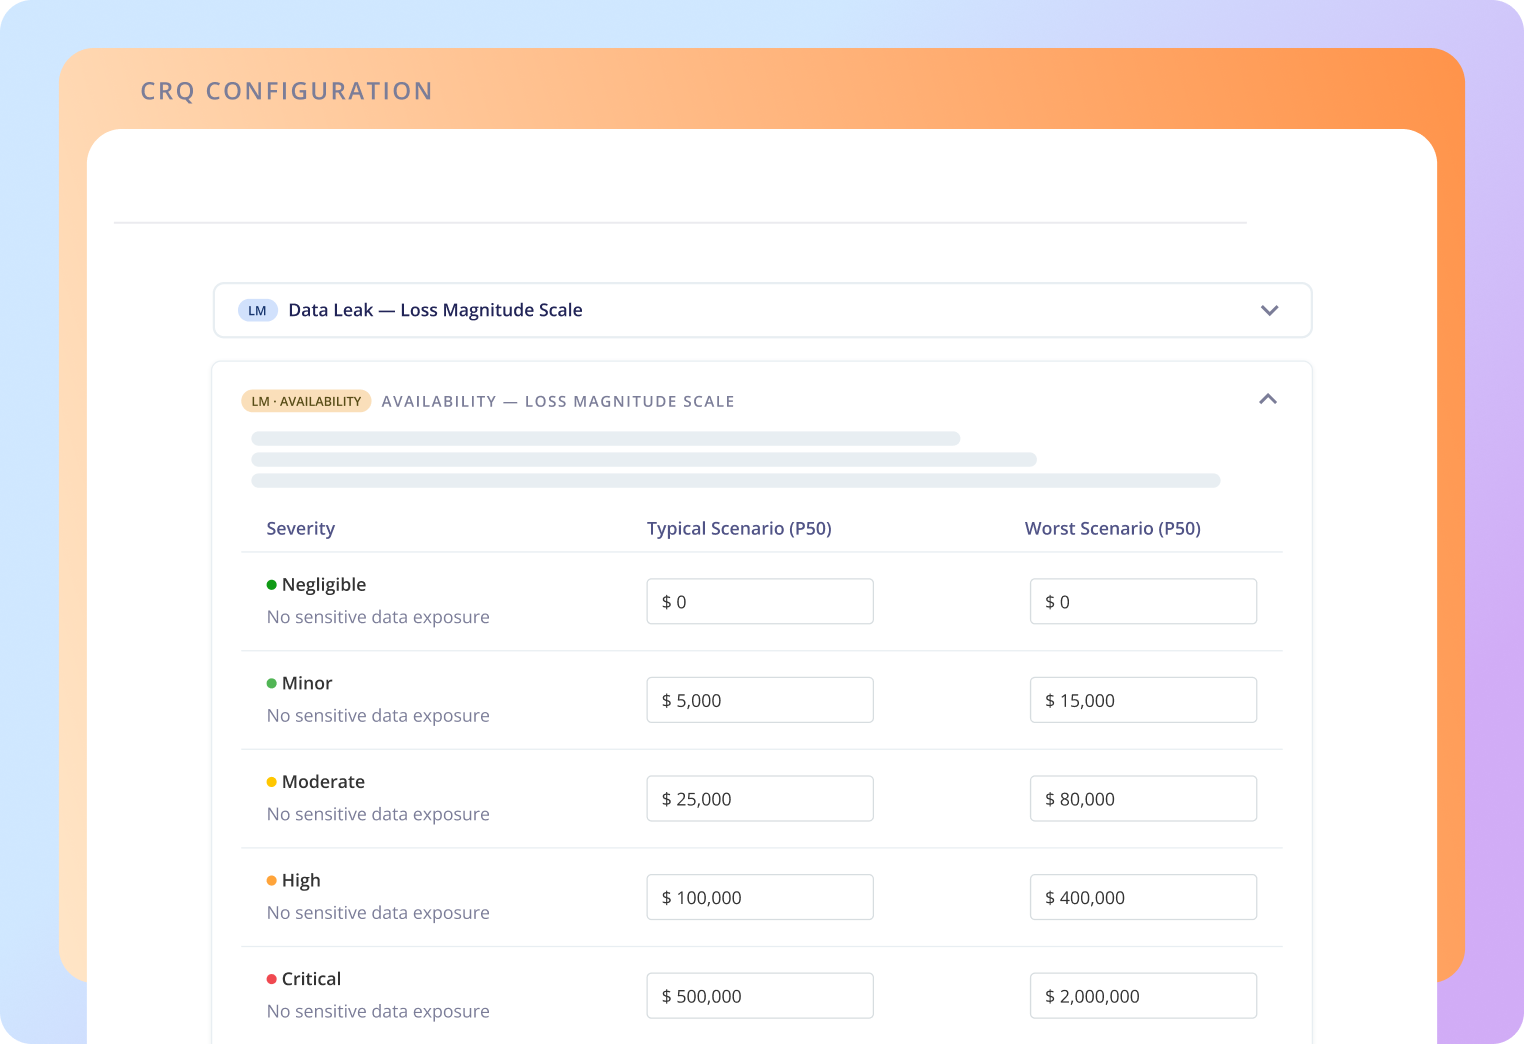
Yes, you can customize the financial impact assumptions to align with your organization’s risk appetite, policies, and business context.
-
CRQ uses financial loss ranges to reflect uncertainty and provide more realistic estimates rather than false precision.
-
Yes, CRQ provides portfolio-level visibility into potential financial exposure across your third-party ecosystem.
-
CRQ supports security, TPRM, risk, and business leaders who need to prioritize risk and make informed investment decisions.
-
CRQ translates cyber risk into financial terms, making it easier to communicate potential business impact and support informed decisions.